

-
Warehouse Insight
-
-
- Overview
- Hardware and Software Requirements
- Business Central Object Import and Merge
- Business Central Data Configuration
- Warehouse Insight Barcode Objects
- Warehouse Insight Web Service Installation
- Android Scanner Install
- Windows Scanner Installation
- Configuring the Software
- Uninstalling the Solution
- Modified Business Central Objects
- Source Versions
- Configure Business Central On-Premises Device Licenses
-
- 1. Introduction
- 2. Overview
- 3. Main Landing Page
- 4. Item Inquiry
- 5. Bin Inquiry
- 6. Advanced Inventory Count
- 7. Basic Count
- 8. Receiving
- 9. Put-Aways
- 10. Ad-Hoc Movements
- 11. Directed Movements
- 12. Picking
- 13. Shipping
- 14. Production Order Consumption
- 15. Production Order Output
- 16. Assembly Orders
- 17. License Plates
- 18. Scratchpad
- 19. Configuration
- Push Warehouse Insight Updates to Devices
-
- Print From Warehouse Insight
- DataLogic Falcon WiFi Configuration
- Controlling the Beep Sound Effect on DataLogic Scanners
- Warehouse Insight with NTLM Authentication
- Configure Windows Scanner for Business Central SaaS
- Connect Warehouse Insight Desktop Client to Business Central Cloud
- Datalogic Falcon X3 Scanner Timeout
- Clone Warehouse Insight Service for Business Central On Prem
- Configure Windows Scanner for Business Central On Prem
- Ad Hoc Move Module
- Display a Custom Image on Your Device
- Configure Scanner Settings for Memor 10/20 and Skorpio X5
- OAuth Login Options for Warehouse Insight 2.8
- Item Barcode Rules
- Set Up the Windows Desktop Client for Oauth (SaaS)
- Azure Active Directory (AAD) OAuth Configuration for Warehouse Insight 2.8+
- Change Locations on the Handheld Devices
- Barcode Symbology and Encoding
- Configure Data Caching in Warehouse Insight
- Configure OAuth Guest Tenant or GDAP Login for Warehouse Insight
- Configure Scanner Settings for Zebra
- Configure Scanner Settings for Honeywell
- Configure Scanner Settings for CipherLab
- Capture an Image on a Scanner Using Warehouse Insight
-
- Add Purchase Order Comments From Your Handheld
- View Purchase Order Comments on Your Handheld
- Capture Image on Sales Order
- Attaching Documents from the Scanner
- Ship and Invoice Sales Order
- Overriding Base Application Events via Design
- Sample Offline Application
- Sample Quantity Dialog Extensions
- Factboxes
- Over-Receiving from Handhelds
- Read barcodes Configured in LS Retail into Warehouse Insight
- Add Signature Capture to Warehouse Insight
- Use the Application Wizard in Warehouse Insight
-
- Proof of Delivery
- Fixed Asset
- Over Picking
- Inventory Quantity Adjustment
- Warehouse Insight Private Add-On Catalog
- Subcontract Receiving
- Two Stage Inventory Pick
- Warehouse Insight Quality Inspector Integration
- Post and Print Outbound Orders
- Ship-Post and Invoice
- Embedded License Plate
- Update Warehouse Receipt Bin
- Warehouse Insight Shop Floor Integration
-
WMS Express
-
License Plating
-
Dynamic Ship
-
- Configuring Dynamic Ship in Business Central
- Data Requirements for Dynamic Ship
- Overview
- Configuring EasyPost
- Get Started with Dynamic Ship
- Dynamic Ship Permissions
- Dynamic Ship Carrier Account Configuration
- How the Dynamic Ship Carrier is linked to the Business Central Shipping Agent
- How to Add Predefined Packages for Carriers
- Carrier Service Configuration Packages
- Set Up Carrier Loomis
- Canada Post Third Party Billing
- Enabling UPS SurePost on your EasyPost account
- Configure a UPS Digital Access Program Account
- Set Up Dynamic Ship Email
- Configure and Use Scales
- Enable and Use the External Rate Entry
- FedEx Commercial Invoice Requires Electronic Letterhead
- Freight Price Rules
- Create a Free Freight Campaign
- Generate Serial Shipping Container Code (SSCC)
- Add an International Shipping Address
- Override Customer Contact Source in Dynamic Ship
- Set USPS Media Mail Special Rate in Dynamic Ship
- Add the Certificate of Origin Report
- Dynamic Ship Go Live Checklist
- Order Packaging Setup
- Email Error Logging in Dynamic Ship
- Automated Tracking Updates in Dynamic Ship
- Address Requirements in Dynamic Ship
- Redirect to Warehouse Shipment with Dynamic Ship
- Preview Preferred Commercial Invoice in Dynamic Ship
-
- Dynamic Ship Process
- Use the Package Worksheet in Dynamic Ship
- Order Packaging in Dynamic Ship
- Use Quick Label in Dynamic Ship
- Create and Print Return Labels in Dynamic Ship
- How to Generate a Shipment Manifest
- Manifesting USPS Shipments
- Create a Freight Quote
- Create a Shipping Label for a Miscellaneous Shipment
- Copy Last Package
- Use Address Validation
- Use Pack Commands
- Item Tracking Lines and Overpacking in Dynamic Ship
- Inbound/Outbound and Return Label Enhancements in Dynamic Ship
-
- Create License Plate Templates
- Package Options
- Label Placeholders - Package Options
- Service Endorsement Options
- Bill Shipping Fees to a Customer's Account
- Payment Types for Alternate Billing
- Include Extra Text on Shipping Label
- Blind and Double Blind (Drop) Shipments
- Configure Customer Options
- Tax Identifiers
-
- How the Customs Information is Populated
- Reprint Shipping Labels using Dynamic Ship
- Include COD Charges with Shipping
- Zebra High Quality Print
- Ship Non-Regulated Hazardous Material
- Ship with Saturday Delivery
- Print Bill of Lading Report
- Chain Multiple Pack Commands
- Find Shipment and Package Tracking Numbers
- Assign Outbound Serial Number at Shipping Time
- Refund Shipment Label
- Actual Shipping Cost
- Pack Item Variants
- Respecting External Freight Costs
- Reconcile Carrier Invoice
- Role Tailored Client Shipping Scale Integration
- No Rates Returned For A Shipment
- Retrieve an Order ID
- Shipper Number Cannot Be Used
- Package Worksheet: Clear Address Cache
- Warehouse Shipment Posting Error
- USPS Ground Advantage
- Serial Shipping Container Code (SSCC) Labels
-
Shop Floor Insight
-
- Daily Time Report for Payroll Administrator
- Shift Scheduling with Shop Floor Insight
- Routing Step with Shop Floor Insight
- Color Coding Time Cards
- Production Order Assignment with Shop Floor Insight
- Streamline Processes with Work Instructions
- Cleaning up Barcodes in Business Central
- Configurable Business Central Payroll Export for ADP and other Payroll Solutions
- Production Dispatch Lists that Boost Efficiency
- How to use the Shop Floor Production Order job report as your default production order job card report
- How to Print Barcodes for Job Tasks in Shop Floor Insight
- How to automatically round time card line entries
- How to Print Barcodes for Production Order Operations
- How to record a quality inspection when output data is captured
- How to display the Shop Floor Insight Approver role in the "Explore All" page
- Shop Floor employees are having their shifts end prematurely
- How to record a quality inspection when a scheduler item is moved
- How to ensure supervisors only see time cards of their workers for approval
- Fix a "Company not licensed" error message in Shop Floor Insight
- Adding a New Employee & Printing a Barcoded Badge
- Filtering Production Orders on the Dispatch List in Shop Floor Insight
- How to Record Consumption
- How to Record Output
- The Supervisor / Employee Relationship
- Using Links in Shop Floor Insight
- Client Configuration Cards
- Shop Floor Activities
- Line Coloring
- How to Record a Comment
- Printing a Production Order Job Card
- Quality Inspections when Recording Output
- Changing the Work or Machine Center by Scanning a Barcode
- Dispatch List Filtering
- Automatically Assign Work and Machine Centers
- Time Card Line Rounding for Job Tasks
- Line Rounding of First Time Card Line
- Time Card Approval Process and Worksheet
- Include Other Paycodes for Overtime Calculations
- Automatic Filler Time Functionality
- Time Card Line Rounding for Shift Breaks
- Output to License Plate
- Production Order Analysis, Investigation, and Reporting Options in Business Central
-
- How to use the Shop Floor Production Order job report as your default production order job card report
- Shop Floor Insight Language Configuration
- Clock In Early to Midnight Shift using Shop Floor Insight
- Configure OAuth for Shop Floor Insight 7.8
- Fields Included in Shop Floor Insight’s Search Field
- Access and Configure Service-to-Service Authentication in Shop Floor Insight
- Configure Shop Floor Insight for automatic time splitting scenarios
- Shop Floor Client Configuration Cards Recommendations
- Configure OAuth Service-to-Service Connections in Shop Floor Insight
- Upgrading Shop Floor Insight Quality Inspections to use Quality Inspector
- De-Select a License Plate in the Shop Floor Insight Web Client
- Shop Floor Insight 7.12 with Quality Inspector and Job Tasks
- Modify the Shop Floor Insight Client Credentials
- Developer guide to Custom Shop Floor Insight badges and Printing Shop Floor Insight employee badges outside of Business Central
- Shop Floor Insight Security and Compliance Information
- Shop Floor Time Card Validation Rules
- Shop Floor Setup page
- Allocating Internal Labor Costs Using Projects and Shop Floor Insight
- How to Change the Date Format on the Shop Floor Insight client
- Example Line Rounding Rule for Lunch Breaks
-
- 1. Before you Begin with Shop Floor Insight
- 2. Installing Shop Floor Insight
- 3. Registering Shop Floor Insight
- 4. Configure Special Permissions in Shop Floor Insight
- 5. Configure Paycodes in Shop Floor Insight
- 6. Configure Activity Codes in Shop Floor Insight
- 7. Configure Shifts in Shop Floor Insight
- 8. Configure Shop Floor Employees in Shop Floor Insight
- 9. Configure Work Centers in Shop Floor Insight
- 10. Configure Client Configuration in Shop Floor Insight
- 11. Configure Time Zone in Shop Floor Insight
- Install and Configure Shop Floor Insight (SaaS)
- 13. Print Barcodes and Smoke Test in Shop Floor Insight
- How to do an upgrade to the Shop Floor Insight Windows service
- Shop Floor Insight Communication App Requirements
- Set Up Facial Recognition
- Install and Configure Shop Floor Insight (On Prem)
- How to Print Non-Productive Activity Codes (such as Lunch and Break) in Shop Floor Insight
-
- 1. Before You Begin with Shop Floor Insight
- 2. Navigating Business Central in Shop Floor Insight
- 3. Process Overview in Shop Floor Insight
- 4. Printing Barcodes in Shop Floor Insight
- 5. Tour of the Shop Floor Interface
- 6. Capture Shop Floor Data for Production Orders in Shop Floor Insight
- 7. Capturing Job Time in Shop Floor Insight
- 8. Closing Time Cards in Shop Floor Insight
- 9. Approving Time Cards in Shop Floor Insight
- 10. Calculate Overtime in Shop Floor Insight
- 11. Posting Shop Floor Data in Shop Floor Insight
- 12. Export Time in Shop Floor Insight
- Configure Output Clock on Behavior
- Add a Non-Productive Activity Code
- Shop Floor Insight: Use the Mobile Interface Without a Phone
- Shop Floor Insight: Shop Floor Native Phone Client
- Shop Floor Insight's Published Events
- Group Time Cards in Shop Floor Insight
- How to Report on Operators that did not Clock Off with Shop Floor Insight
- Shop Floor Work Type Rules
- Creating Multiple Time Cards with the Time Card Creation Wizard
-
- How to Record Consumption
- Filtering Production Orders on the Dispatch List in Shop Floor Insight
- Adding a New Employee & Printing a Barcoded Badge
- How to Record Output
- The Supervisor / Employee Relationship
- Using Links in Shop Floor Insight
- Client Configuration Cards
- Shop Floor Activities
- Line Coloring
- How to Record a Comment
- Printing a Production Order Job Card
- Quality Inspections when Recording Output
- Changing the Work or Machine Center by Scanning a Barcode
- Dispatch List Filtering
- Automatically Assign Work and Machine Centers
- Time Card Line Rounding for Job Tasks
- Line Rounding of First Time Card Line
- Time Card Approval Process and Worksheet
- Include Other Paycodes for Overtime Calculations
- Automatic Filler Time Functionality
- Time Card Line Rounding for Shift Breaks
-
- 401 Error Messages in Shop Floor Insight
- Troubleshoot Shop Floor Insight Issues
- How to troubleshoot "(400) Bad Request" errors in Shop Floor Insight
- Shop Floor Insight: Error Messages and Fixes
- Resolve URL ACL Issues
- Troubleshoot SSL Certificate
- Shop Floor Insight Production Go-Live Checklist
- Troubleshoot Zero Run Time Entries on Shop Floor Time Cards
-
Advanced Inventory Count
-
- Introduction: Advanced Inventory Count
- 3. Module Design
- 4. Performing a Full Count
- 5. Performing a Cycle Count
- 6. Inventory Counts with WHI
- 7. Appendix A – Report Options
- Setting Inventory Count Card As-Of-Date
- Setting Locations on the Count Card
- Setting Lot/Serial Number Tracking
- Setup of Posting Count Options
- Setting up Recounts in Inventory Count Module
- Reconciling the Count in Inventory Count Module
- Posting the Inventory Count
- Inventory Count Bin Blocking Options
- Calculating Count Period Codes
-
Counter Sales
-
-
- Payment Providers in Counter Sales
- Payment Provider Configurations in Counter Sales
- Payment Provider Selection Logic in Counter Sales
- Payment Networks in Counter Sales
- Set Up Payment Provider Extension EBizCharge in Counter Sales
- Set Up Payment Provider Extension Clover in Counter Sales
- Set Up Payment Provider Extension Moneris in Counter Sales
- Overview
- User Permissions
- Profiles (Roles)
- Counter Sales Setup
- Counter Sales Users
- Payment Methods
- Customer Accounts
- Reason Codes
- Take Order Wizard
- Counter Sales Orders
- Quick Scan
- Return Order Wizard
- Counter Sales Return Orders
- Price Check
- Enhanced Item Search
- Enhanced Contact Search
- My Locations
- Related Items
- Price Overrides
- Lost Sales
- Special Order Items
- Daily Close
- Contact Sales History
- User Salespersons
- Set up Star TSP Printers for Receipt Printing for Counter Sales
- Set up Epson TM-T88 Printers for Receipt Printing for Counter Sales
- Use Gift Cards in Counter Sales
- Use Cash Drawers / Registers in Counter Sales
-
-
Product Configurator
-
- Version Information
- Product Configurator Configurations
- Product Configurator Item Category
- Product Configurator Choice Combination
- Product Configurator Option Choice
- Product Configurator Bulk Edit
- Product Configurator Options
- Product Configurator BOM
- Use Quoting Items
- Additional Choices in Product Configurator
- Use Check Configuration
- Use Line Type and Indent Options
- Update Routing Run Times
- Add Option Choice Comments
- Use Rule Builder
-
- 1. Application Description
- 2. Installation
- 3. Using the Product Configurator
- Text Template Variables
- Update Lookup Display Order in Product Configurator
- Copy Values in Product Configurator
- Choice Sets in Product Configurator
- CALLEDFROM Variables in Product Configurator
- Rule Builder Lookup Configurations in Product Configurator
-
NavXtender
-
- Articles coming soon
-
- Install NavXtender
- Add Languages in NavXtender
- Having Issues?
- SharePoint Support
- Why am I having troubles accessing SharePoint via UNC?
- Why is the drag and drop not working, or NavXtender button not visible?
- Are you using an anti-virus application?
- Do I need to install NavXtender on every computer?
- I still need help. Who can provide technical support?
- I would like to use NavXtender with my custom pages. How do I do that?
- NavXtender Language Support
- NavXtender Web Service Authentication 401
- NavXtender Web Service Troubleshooting
- Should I install the 32-bit or 64-bit version of NavXtender?
- What changes does NavXtender make to Microsoft Dynamics NAV?
- What is the difference between the stand-alone and integrated version of NavXtender?
- What versions of Microsoft Dynamics NAV is NavXtender compatible with?
- Why am I getting a permissions error?
- Item Attribute Mapping in Product Configurator
-
DocXtender
-
Barcode Generator PowerTool
-
PrintNode Connector PowerTool
-
Miscellaneous
-
Graphical Scheduler
-
- Exploring the Graphical Scheduler Screen
- Changing the production schedule of an operation
- The Graphical Scheduler Views
- Applying a Filter
- Modifying the Dates and Zoom
- Modifying the Graphical Scheduler Settings
- Use the Is Late field
- Graphical Scheduler: Use the Warehouse Pick Assignment Feature
- Sort Work Centers and Machine Centers
- Change the Production Order Status from the Graphical Scheduler
- Display Firm Planned and Planned Production Orders in Graphical Scheduler
- Anything Feature in Graphical Scheduler
- Display Service Order Allocations in Graphical Scheduler
- Default a Time Frame in Graphical Scheduler
- How to Visualize Sales Orders Grouped by Location in the Graphical Scheduler
- Configure and Use Date Presets in Graphical Scheduler
- Graphical Scheduler API, how to use the JSON directly for a custom Gantt chart
- Allowing Changes with the Graphical Scheduler Anything Data Source
- How to Visualize Work Center Capacity and Load in Graphical Scheduler
- Graphical Scheduler How to Show Work Center Operations Grouped By Production Order No.
-
MxAPS
-
- Introduction
- Generate an MxAPS Schedule
- Production Cells
- Setup
- Delay Increment
- Scheduling Configurations
- Scheduling Rules
- Scheduling Rule Card
- Scheduling Rule Parameters
- Segment Codes
- Alternate Group List
- Alternate Group Card
- Schedule Result List / Schedule Results
- Schedule Result
- Order Schedule List
- Machine Load Details
- Operation Schedules
- Order Attribute Schedules
- Commit Results
- Result KPI FactBox
- Schedule Rule Details
- Machine Alternate Constraints
- Mx Item Card extends Item Card
- Resource Requirements
- Machine Constraints
- Machine Transfers
- Shop Calendar Exceptions
- Configure Azure Storage for MxAPS
- Production BOM Component Constraint Setup
- How to use setup eliminations to reduce setup time
- How to Identify Material Shortages in an MxAPS Schedule
- How to identify which production orders are shown in the Machine Schedule Summary
- Configuring Native Setup Eliminations
- Inventory Availability Constraints for Multi-Level BOMs with MxAPS
- Understanding Idle Allowance vs. Absolute Allowance in MxAPS
- How MxAPS Uses Inventory During Scheduling
- Understanding the Machine Schedule Summary in MxAPS
- Understanding Why MxAPS Moved My Production Order
- How MxAPS Reduces Changeovers
- Understanding MxAPS Lead Time, Fence Type, and Material Availability
- Does MxAPS Schedule Forward or Backward
- Which Production Order Statuses Should I Include in an MxAPS Schedule?
- How to Configure a Rush Order in MxAPS
- How to Modify an MxAPS Schedule
- Preventing Lower-Ranked Orders from Filling Schedule Gaps
- Troubleshooting Unexpected Results in MxAPS
- Using Tooling and Labor as Secondary Constraints in MxAPS
- How MxAPS Handles Schedule Changes, Manual Moves, and Long-Lead-Time Orders
- Using Work Centers with Interchangeable Machine Centers in MxAPS
- Grouping Production Operations into Order Sets in MxAPS
- Sequencing Similar Jobs and Reducing Changeovers in MxAPS
- Configure a Read-Only View in Graphical Scheduler
-
Enhanced Planning Pack
-
- Enhanced Plan Vendor Summary
- Enhanced Forecasting Worksheet
- Item Planning Review
- Multi-Level BOM Viewer
- Routing Analysis
- Enhanced Planning Worksheet
- Configure the Sales and Inventory Forecast for the Enhanced Planning Pack
- Item Planning Review: Customize the Entry Types
- Enhanced Forecasting Worksheet: Customize the Predicted Value and Change Item Planning Expressions
- Change Orientation of the Multi-Level Bill of Material Visualizer in Enhanced Planning Pack
- Create Custom Views in Enhanced Planning Worksheet and Order Fulfillment Worksheet
- How does the Planning Worksheet Purchase Plan calculate the amount to purchase?
- Planning Concepts and Parameters in the Enhanced Planning Worksheet
- Excluding Expiring Inventory from Purchase Planning on the Enhanced Planning Worksheet
- How to Plan Purchases for Demand Across Multiple Locations
- How to Use Scheduled Routing Analysis Results
- How Reordering Policies Affect the Enhanced Planning Worksheet
- How Forecasts Affect the Enhanced Planning Worksheet Purchase Plan
- How To Configure Item Planning Review to Calculate Usage from Specific Item Ledger Entries
- Plan Purchases for Multi-Level Components Using Finished-Item Forecasts
- Trace Raw Material Demand Through a Multi-Level BOM in Enhanced Planning Pack
- How to Identify the Source of Demand in the Enhanced Planning Worksheet
- Analyzing Production Order Variances with Production Order Analysis
- Production Order Analysis, Investigation, and Reporting Options in Business Central
- Enhanced Planning Pack Integration Events
-
Order Ship Express
-
Order Fulfillment Worksheet
-
- Introduction
- Recalculate Availability with the Order Fulfillment Worksheet
- Automatic Reservation with the Order Fulfillment Worksheet
- Split Allocation with the Order Fulfillment Worksheet
- Create Warehouse Shipments with the Order Fulfillment Worksheet
- Create Picks with the Order Fulfillment Worksheet
- Use the Pick Worksheet in the Order Fulfillment Worksheet
- Assemble to Order with the Order Fulfillment Worksheet
- Order Fulfillment Worksheet Published Events
- Order Fulfillment Worksheet Statuses
- Create Custom Views in Enhanced Planning Worksheet and Order Fulfillment Worksheet
- Create and Edit a Custom View in the Order Fulfillment Worksheet
- Create and Edit an Advanced Line Filter in the Order Fulfillment Worksheet
- Use the Movement Worksheet in the Order Fulfillment Worksheet
-
Import Export PowerTool
-
Quality Inspector
-
- Configure Grades
- Validate Production
- Automate Production
- Enable Functionality Per Quality Inspector
- Create Quality Inspections for Receipts
- Quality Inspector’s Published Events
- Set Up and Configure Azure Blob Storage and Azure Document Intelligence with Quality Inspector
- Create a Test Based on a Vendor
- Use Auto Output Configuration in Quality Inspector
- Filter by Item in Quality Inspector
- Create a Receiving Rule in Quality Inspector
- Create Automatic Tests for Sales Returns Without Warehouse Receipts in Quality Inspector
- Create a Warehouse Movement Rule in Quality Inspector
- Create a Production Rule in Quality Inspector
- Select which Tests are Considered when Evaluating Lot Grade Restrictions in Quality Inspector
- Reference a Field from an Item Card or an Item Attribute in Allowable Conditions or Pass Conditions
- Set a Database Value in a Workflow Response
- Restrict a Field’s Choices Using Another Field Using Quality Inspector
- First Article Inspection Report (FAIR Form 3)
- Schedule Automated Tests with Quality Inspector
- Use Field Level Work Instructions in Quality Inspector
- Use Test Generation Rule Trigger to Automate Creation of Quality Inspection Tests
- Use Assembly Output Integration in Quality Inspector
- Override a Test Grade Using Best Practices in Quality Inspector
- Configure Periodic Tests in Quality Inspector
- Configure Periodic Tests on any Lots Within a Certain Container in Quality Inspector
- Create a Test Generation Rule for a Specific Item in Quality Inspector
- Available User Interfaces for Recording Quality Inspections
- Create a Test Generation Rule for a Category of Items in Quality Inspector
- Capture the Container (Vat/Vessel/Bin) from the Production Order when a Test is Made from a Production Order in Quality Inspector
- Automate Test Creation when Posting a Purchase Receipt with Warehouse Handling
- Enable Purchase Order Release Integration in Quality Inspector
- Use the Sample Source feature on the Quality Inspector Template
- Quality Inspectors' and Quality Inspection Permissions
- Quality Inspector Setup
- Skip-Lot Thresholds in Quality Inspector
- Quality Inspectors and Quality Inspection Permissions Page
- Implement CFR Section 42 Subpart C while using Quality Inspector
- Implement a "Test Every 'X' Lots" Scenario with Skip-Lot in Quality Inspector
- Sampling and Skip Lot in Quality Inspector
- Implement Skip Lot with Receiving in Quality Inspector
- Skip Lot Inspections in Quality Inspector
- Create an Inspection Checklist with an Override Checkbox
- Quality Inspection Test Results Matrix
- Quality Inspection Fields
- Move Product from One Bin to Another Bin Automatically in Quality Inspector
- First-off inspections, First Article Inspections, and Initial Production Checks Using Quality Inspector
- Create PDF Attachments Automatically When a Test Finishes in Quality Inspector
- Use Attach as PDF to Automatically Create a PDF of a Certificate of Analysis and Other Quality Inspection Reports
- Use Adaptive Cards in Teams and Power Automate with Quality Inspector
- Quality Inspector Expression Examples
- How to Create a Facility Readiness Check for a Location
- How to Create a Work Station or Production Line Readiness Check for a Work Center
- How to Record Quality Inspection Tests on a tablet, phone, or other mobile device
- Quality Inspector and the Microsoft Quality Management Extension
- Non-Conformance Reports (NCRs) in Quality Inspector 7.26
- Implementing ANSI Z1.4 C=0 Sampling with Quality Inspector
- What is Skip-Lot Inspection?
- Advanced Quality Inspector Source Configuration List
- Quality Inspector Source Configuration Card
- Quality Inspection Grades
- Quality Inspection Test Generation Rules
- Understanding Test Generation Rules and Source Configuration in Quality Inspector
- Performing Quality Inspections Before Serial or Lot Numbers Are Posted
- How to Prevent Receiving a Purchase Order Until a Quality Inspection Test is Completed
- Designing Large Dimensional Inspection Plans in Quality Inspector
- Configuring Nominal Dimensions and Symmetric/Asymmetric Tolerances
- Choosing Where to Store Quality Specifications in Quality Inspector
- Using Special Characters in Quality Inspection Field Choices for Threshold Categories
- Permission Sets for Quality Inspector
- Prevent Production Output Until a Quality Inspection Test Passes
- Set Up and Configure Quality Inspector
- Understand Quality Inspection Templates and Test Generation Rules
-
- Assign Tests to an Inspector
- Create a Purchase Order Test
- Receiving Automation
- Assign and Review Tests in Quality Inspector
- Create Ad Hoc Quality Tests in Quality Inspector
- Perform Inventory Movement in Quality Inspector
- Create Quality Inspection Template and Connect to a Customized Table in Quality Inspector
- Create a Test Using Test Results in Quality Inspector
- Create a Test in Quality Inspector that is Available with Microsoft Teams
- Block and Unblock Lot Transactions in Quality Inspector
- Restrict the Use of a Lot Transaction When a Test Fails in Quality Inspector
- Manage Image Attachments in Quality Inspector
- Automate Block and Unblock Lot Transactions in Quality Inspector
- Collect Multiple Samples in Quality Inspector
- Set Values with Copilot in Quality Inspector
- Use Numeric Expressions (Calculated Field) in Quality Inspector
- Use embedded expressions within acceptable values and pass conditions
- Look up Specifications from Another Table when Creating Quality Inspection Tests
- Use Tools in Quality Inspector
- Create a Purchase Return Order from a Test in Quality Inspector
- Use Measurement Notes and Comments in Quality Inspector
- Warehouse Insight Quality Inspector Integration
- Take and Attach a Picture to a Quality Inspection Test
- Create a Re-test in Quality Inspector
- Create a Transfer Order to Move Material from a Directed Pick Environment to a Non-Warehouse Location in Quality Inspector
- Move Product Automatically from One Bin to Another Bin in Quality Inspector
- Create and Use a Balloon/Bubble Template in Quality Inspector
- Use Quality Inspection Tests
- Use Quality Inspection Templates
- Use Quality Inspector with Power Automate
- Create a Test Automatically with a Put-Away or Movement into a Bin in Quality Inspector
- Create a Test Automatically on Production Output in Quality Inspector
- Create a Test Automatically with Assembly Output in Quality Inspector
- Add Attachments to Inspection Test Plans and Quality Inspection Tests in Quality Inspector
- Copy Quality Inspection Attachments Automatically in Quality Inspector
- Sample Workflows for Quality Inspector: Moving Items, Initiating a Retest, and Discarding Failed Stock
- Route Put-aways to Inspection Bins in Quality Inspector for QC Hold locations
- Create a Test from Sales Order Production Planning in Quality Inspector
- Attach Files to PDF Non-Conformance Reports in Quality Inspector
- How to require a Quality Inspection Test before moving to the next step in an operation
- Migrate Between Quality Management and Quality Inspector
- Quality Inspector Failure Analysis Tool
- Use Basic Signatures in Quality Inspector
- Recording Notes in Quality Inspector
- Configure Work Instructions in Quality Inspector
- Quality Inspection Test Values
- Quality Inspection Test Results Matrix (duplicate)
- Quality Inspection Sample Worksheet
- Quality Inspection Chart Values
- Select Create Test Behavior and Find Existing Behavior in Quality Inspector
- Create a Multi-Step Approval Workflow to Finish a Quality Inspection Test
- How to Place Part of a Lot On Hold in Quality Inspector
- How to Scan Paper Quality Inspection Forms into Quality Inspector
- Using the Quality Inspector Failure Analysis Tool
- Sample Bulk Receipts of Untracked Items in Quality Inspector
- How Quality Inspector Supports SQF Audit Readiness
- Handle Items That Fail After a Lot Previously Passed Inspection in Quality Inspector
- Create an Ad Hoc Quality Inspection Test for an Item Already in Stock
- Manage COA-Required Purchase Receipts with Quality Inspector
-
Cycle Count Scheduler
-
Safety Logbook
-
Maintenance Manager
-
App Registration
-
- Articles coming soon
-
- Articles coming soon
-
Configure OAuth Service-to-Service Connections in Shop Floor Insight
Note: Use the following instructions when you are:
- on SaaS or are using Microsoft Entra (previously known as Azure Active Directory) authentication,
- and on Business Central 20 or newer,
- and you need multiple connections with different accounts (for scenarios such as multiple time zones),
- or having issues with redirect URLs (sometimes occurs with LS Central environments),
- or you are configuring multiple servers to connect to the same instance for any reason,
- or you want to have improved security and want your Entra application specific to your tenant for more control over access keys.
This article describes how to configure multiple OAuth Service-To-Service (S2S) for multiple Shop Floor Insight windows services. The following instructions are included:
- Create an App Registration in Azure
- Collect the Client Secret, Client ID, and Tenant ID
- Configure the Specialized IDs
- Grant Consent in Business Central
Create an App Registration (Microsoft Entra Application) in Azure
To create an App Registration in Azure, sign in with an account that has the appropriate permissions to create the App Registration. Complete the following to create the entry:
- Navigate and log into Azure (if needed).
- Select More Services to access Azure Active Directory and select App Registrations under the Identity section.
- Select +New registration.
- Input a Name (e.g., ShopFloorInsight-TimezoneA).
- Select Accounts in this organizational directory ([Default Directory] only – Single tenant) under Support account types (limits the use of the app registration to the tenant).
- Configure and register the following Redirect URI (required for Shop Floor Insight):
- Web: https://businesscentral.dynamics.com/OAuthLanding.htm
- Or if using LS Central then configure the following Redirect URI (LS Central only):
- Select Register.
- Navigate to the App registrations and select All Applications.
- Locate and select your new entry.
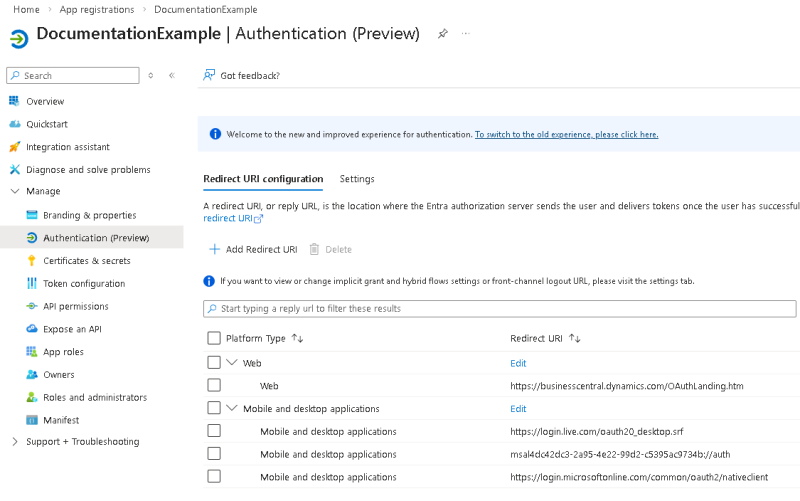
- Select Authentication and select “Add a platform”, or “Add Redirect URI”
- Select Mobile and desktop applications.
- Check the boxes ON for all three entries.
- Ensure the entry below appears:
-
- https://login.microsoftonline.com/common/oauth2/nativeclient
- https://login.live.com/oauth20_desktop.srf
- msal66d9a62b-ddb9-4855-9ed3-361a0515ed2e://auth (generated automatically for the app registration)
- Select API Permissions and select + Add a Permission.
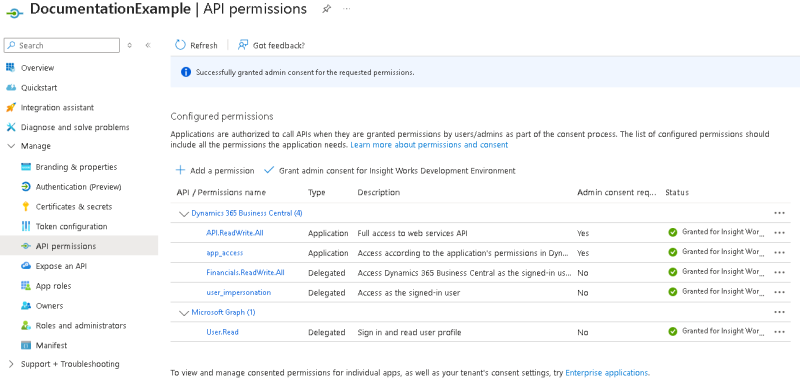
- Locate the Dynamics 365 Business Central and Microsoft Graph boxes and enable both the delegated and application permissions below (gives Business Central access permissions).
| API / Permissions name | Type | Description | |
| Dynamics 365 Business Central (3) | |||
| API.ReadWrite.All | Application | Full access to web services API | |
| app_access | Application | Access according to the application’s permissions in Dynamics 365 Business Central | |
| Financials.ReadWrite.All | Delegated | Access Dynamics 365 Business Central as the signed-in user. | |
| User_impersonation | Delegated | Access as the signed-in user | |
| Microsoft Graph (1) | |||
| User.Read | Delegated | Sign in and read user profile | |
- Grant consent. The button to grant consent might be titled “Grant admin consent for [your organization name here]”.
- If you see this button, but it is not enabled, then you will need to ask your tenant administrator to grant consent for you.
- This still is necessary before proceeding with the remainder of the installation.
- If this step does not occur then you will get authentication errors.
- A successful grant should show all of the API’s permissions that were requests with the green checkbox in the “Status” column.
Collect the Client Secret, Client ID, and Tenant ID
The GUI allows you to create a client secret that expires after two years. For increased security, we recommend using the GUI and having a timed expiry rather than using PowerShell to set up a client secret with an extended expiration date.
Collect the Client Secret
Complete the following to collect the client secret while still in the app registration’s menu:
- Navigate to Certificates & Secrets.
- Select + New Client Secret.
- Input a description and expiry (maximum 24 months).
- Select Add.
- Navigate to Certificates & Secrets.
- Copy the Client Secret Value (Client Secret).
Collect the Client ID and Tenant ID
- Navigate to Overview of the app registration.
- Copy the IDs from the following fields:
- Application (client) ID (Client ID) (this is a GUID)
- Directory (tenant) ID (Tenant ID)
Configure the Specialized IDs
- If the service is already installed:
- Edit the IW.TimeCollectionModule.Service.exe.config file.
- Add the following XML into the settings XML area:
<setting name=”OAuthClientID” serializeAs=”String”>
<value>Put in the client ID collected from the previous steps, this will be a guid</value>
</setting>
<setting name=”OAuthClientSecret” serializeAs=”String”>
<value>Put in the secret value collected from the previous steps</value>
</setting>
<setting name=”OAuthTenant” serializeAs=”String”>
<value>Put in the tenant ID collected from the previous steps</value>
</setting>
- If the service is not yet installed:
- The application ID can be entered in the installation wizard into the “S2S Client ID” field from the “OAuthS2S Client ID” popup from the service installation wizard. Entering the value here will set the “OAuthClientID” field in the configuration XML file.
- The secret collected in the earlier steps can be set in the “Password” field in the “OAuthS2S Client Secret” popup from the service installation wizard. Entering the value here will set the “OAuthClientID” field in the configuration XML file.
Grant Consent in Business Central
When the user selects Grant Consent, the user must have sufficient permissions on the tenant to grant consent. This access might not be available to a Business Central administrator but would be available to the tenant administrator. Contact your IT department if you do not know who your tenant administrator is.
- Navigate to the Azure Active Directory Applications (Microsoft Entra Applications) Card in Business Central.
- Select + New.
- Enter the:
- Client ID: used in App ID (collected in Collect the Client ID and Tenant ID above)
- Description
- Change the state to Enabled.
- Enter the following (minimum) permissions under the appropriate Fast Tab:
- D365 BUS PREMIUM
- IWORKS COMMON
- SFI-SERVICE
- IWX REG REGISTRATION
- IWXQIGENERAL
- LOCAL
- LOGIN
- Sufficient permissions to perform the required Shop Floor Insight tasks (e.g., for jobs, give permissions for jobs; for fixed assets, give permissions for fixed assets; for production orders, give permissions for what they plan on using with production orders).
- Grant consent and follow the prompts (ensure you are logged in with the appropriate administrative user).
4.6 out Of 5 Stars
4 ratings
| 5 Stars | 25% | |
| 4 Stars | 75% | |
| 3 Stars | 0% | |
| 2 Stars | 0% | |
| 1 Stars | 0% |